News
Breaches, threats, advisories and policy: Canadian cybersecurity news, as it happens.
OpenBSD issues urgent advisory targeting OpenSSH vulnerabilities
Cybersecurity authorities have issued a fresh warning regarding OpenBSD systems, highlighting a newly cataloged security advisory designated as AV26-1130. The alert focuses on vulnerabilities impacting OpenSSH versions prior to 10.6p2, prompting system administrators worldwide to audit their network environments and expedite patching procedures.
PHP2Shell: active exploitation reports
Canadian cybersecurity engineering and incident response teams managing large-scale web application infrastructure are racing to address ongoing threat activity following reports of active exploitation targeting the PHP2Shell vulnerabilities (CVE-2026-109618 and CVE-2026-109619).
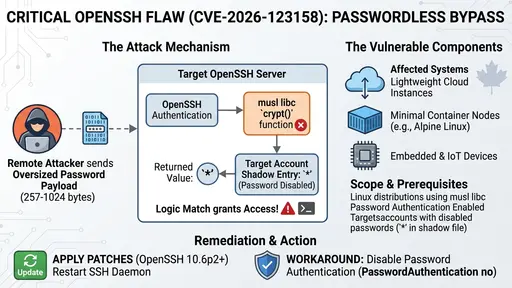
Critical OpenSSH authentication bypass exposes lightweight Linux infrastructure
Canadian systems administrators and security operations teams managing lightweight cloud infrastructure and container environments are facing an urgent emergency patch cycle following the disclosure of a critical authentication bypass vulnerability in OpenSSH
Debian and Ubuntu APT flaw lets MitM attackers swap verified packages and run code as root
A high-severity vulnerability discovered in the Advanced Packaging Tool (APT), the primary package management ecosystem powering Debian, Ubuntu, and their vast network of derivative Linux distributions, leaves unpatched systems susceptible to remote code execution with full administrative privileges.
Burnaby school district data leak
The ongoing digital crisis facing Canada’s educational sector has taken a severe turn as the notorious, Russia-linked Qilin ransomware group published a massive stolen database belonging to the Burnaby School District (School District 41) on the dark web.
Third-party software breach at Williams Food Equipment
The breach, which involved unauthorized data access and extraction between September 13 and September 17, has drawn attention to third-party software dependencies across Canadian online retail.
Cisco advisory AV26-1127 warns of active SD-WAN and Secure Firewall zero-day exploitation
The advisory details an escalating threat environment where unauthenticated remote actors are exploiting flaws across Cisco Catalyst SD-WAN networks and Cisco Secure Firewall Remote Access SSL VPN services
Two Canadian Nationals Indicted in U.S. Federal Court
A 35-year-old Canadian man has been extradited to the United States to face federal criminal charges in connection with a multi-year cyber-intrusion and illegal crypto-mining campaign targeting higher-education networks and academic super-computing infrastructure across four U.S. states.
British businesses caught in Europe-wide supermarket fridge attacks
Three weeks after hundreds of French grocery stores lost refrigerated stock, a new wave of attacks has reached stores in at least 11 European countries. Investigators still don’t know who is behind them. The way in looks familiar: old controllers, connected to the internet, some still on default passwords.
GitLab issues urgent patch
Cybersecurity teams around the world are rushing to update their software deployment pipelines following the release of an emergency security patch by GitLab Inc. The vulnerability, designated as CVE-2026-97229, carries a maximum possible Common Vulnerability Scoring System rating of 10.0 out of 10
Canadians say they can spot scams. Their habits say otherwise.
New Equifax Canada and Bell Cyber surveys show Canadians are confident about spotting scams while weak password and MFA habits persist.
Ottawa finally has a security strategy
It took Canada 22 years to write a new national security strategy. The last one came out in 2004, before smartphones, before ransomware gangs ran like businesses and long before an AI model could find a flaw in code that runs most of the web. So when the federal government released The Plan for a Stronger Canada: National Security for Canadians on Oct. 29, the first reaction in the security community was relief. The second should be impatience.